Professional Ethical Hacking Track (PEHT)
Professional Ethical Hacking Track (PEHT) — a hands-on offensive security program covering reconnaissance, scanning, exploitation, and post-exploitation techniques used by real-world attackers.
 Mo'tasem Abu Baha'
- Beginner
- 22 modules
- 1 lesson
- ~50h
- Arabic & English
- Updated Oct 2026
What you'll learn
- Perform reconnaissance and network scanning
- Enumerate services and identify vulnerabilities
- Exploit systems and escalate privileges in lab environments
- Identify common web application attacks including SQL Injection
- Apply ethical hacking methodology and document findings professionally
About this course
The Professional Ethical Hacking Track (PEHT) is a comprehensive, practice-driven course designed to build real offensive security skills from the ground up. Students progress through the full attacker methodology — information gathering, network scanning, enumeration, vulnerability assessment, exploitation, privilege escalation, and post-exploitation — using industry-standard tools and hands-on labs in a controlled environment.
Rather than focusing on theory alone, PEHT emphasizes practical application: every concept is reinforced with real lab exercises that mirror how attacks unfold in production environments. By the end of the track, students will understand how systems are compromised, how to think like an attacker, and how to translate that knowledge into effective defensive strategies.
Curriculum
22 modules · 1 lesson · ~50h total
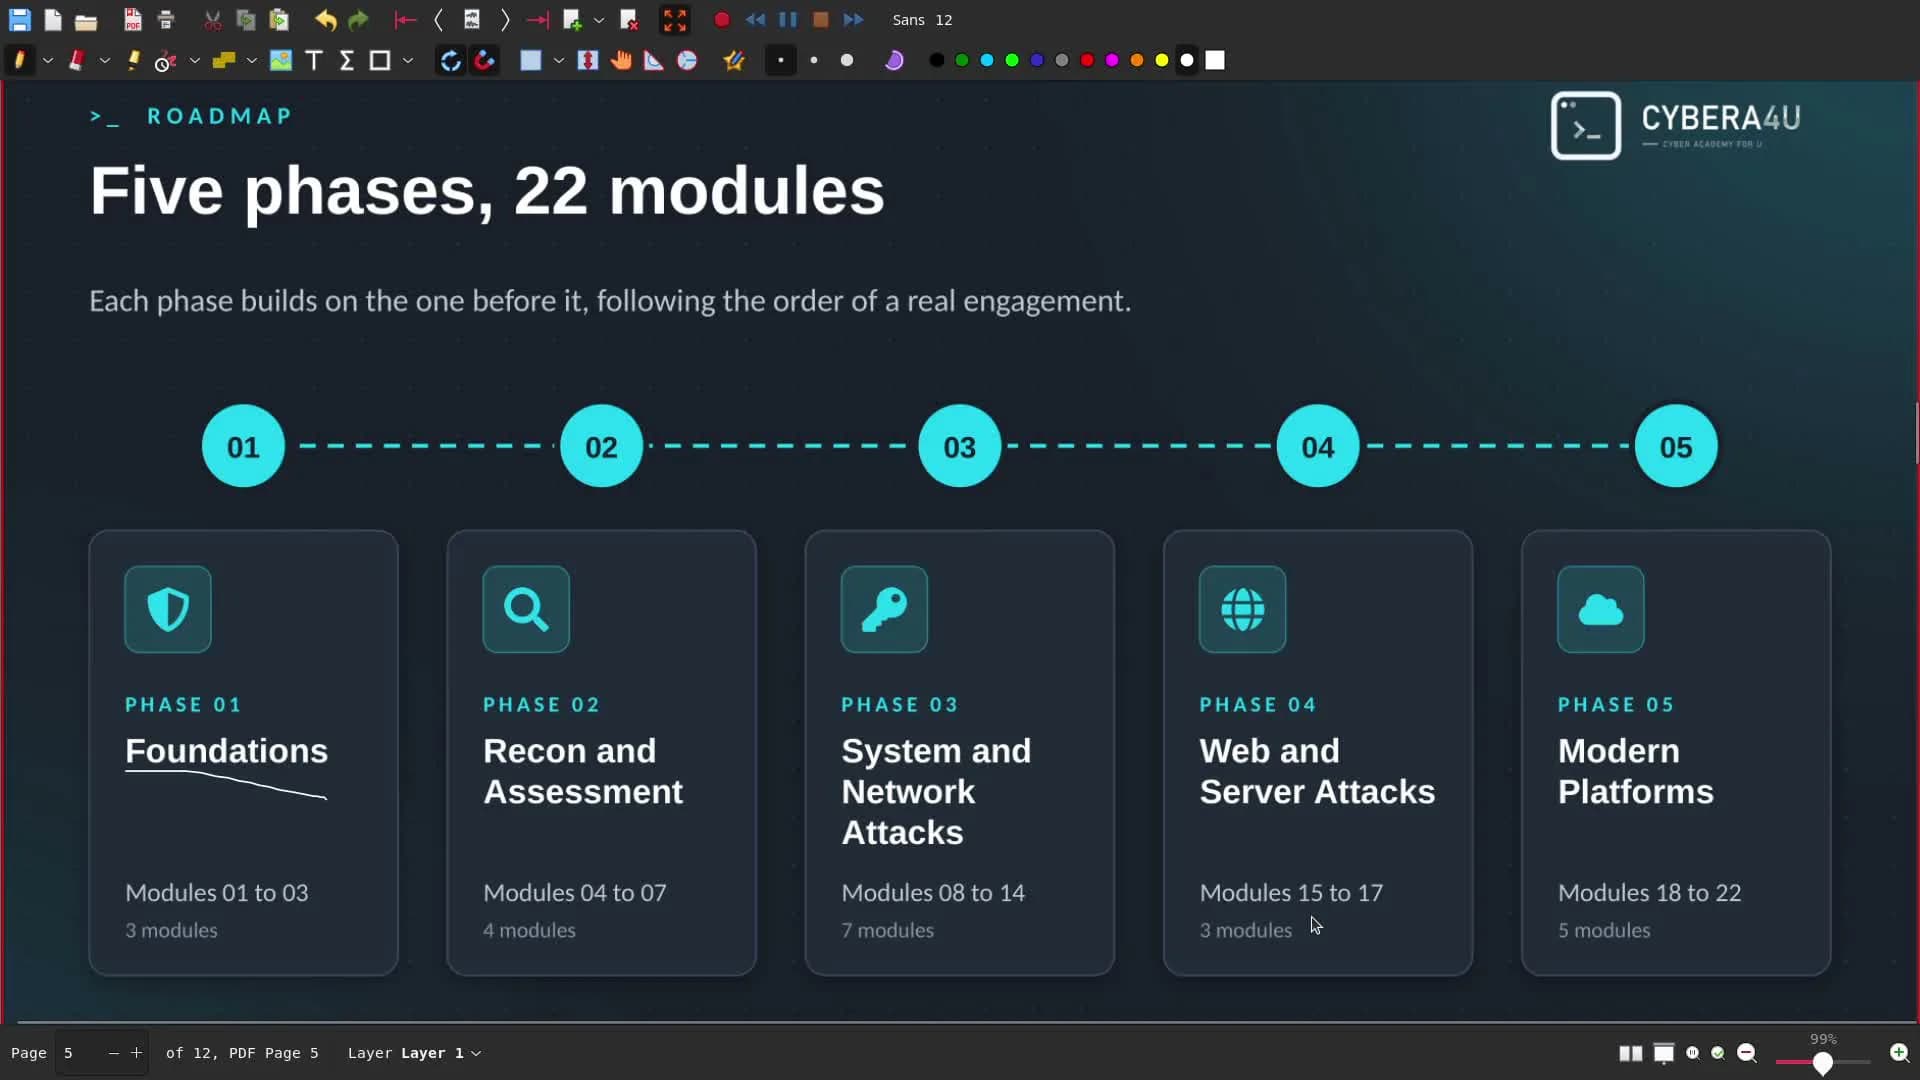
1Module 1: Foundations of Cybersecurity and Ethical Hacking6 lessonsBeing recorded
2Module 2: Building the Practice Lab4 lessonsBeing recorded
3Module 3: Command Line Mastery for Security Testing6 lessonsBeing recorded
4Module 4: Information Gathering Techniques10 lessonsBeing recorded
5Module 5: Network Discovery and Mapping8 lessonsBeing recorded
6Module 6: Service and Resource Enumeration8 lessonsBeing recorded
7Module 7: Identifying and Assessing Weaknesses7 lessonsBeing recorded
8Module 8: Gaining and Maintaining System Access4 lessonsBeing recorded
9Module 9: Malicious Software Concepts8 lessonsBeing recorded
10Module 10: Traffic Interception Techniques4 lessonsBeing recorded
11Module 11: Human-Focused Attack Techniques5 lessonsBeing recorded
12Module 12: Service Disruption Attacks5 lessonsBeing recorded
13Module 13: Communication Session Attacks5 lessonsBeing recorded
14Module 14: Bypassing Security Monitoring Systems8 lessonsBeing recorded
15Module 15: Server-Side Attack Techniques5 lessonsBeing recorded
16Module 16: Web Application Attack Techniques5 lessonsBeing recorded
17Module 17: Database Query Injection Attacks5 lessonsBeing recorded
18Module 18: Wireless Network Attack Techniques5 lessonsBeing recorded
19Module 19: Mobile Platform Attack Techniques6 lessonsBeing recorded
20Module 20: Connected Device and Industrial System Attacks4 lessonsBeing recorded
21Module 21: Cloud Environment Attack Techniques8 lessonsBeing recorded
22Module 22: Applied Cryptography and Attacks4 lessonsBeing recorded
Requirements
- Basic computer skills
- Basic networking knowledge
- Basic Linux knowledge
- Interest in cybersecurity
Who this course is for
- ybersecurity beginners
- IT students
- Security enthusiasts
- Aspiring penetration testers
- SOC and security professionals
- Ethical hacking learners
Your instructor

Mo'tasem Abu Baha'
Cybersecurity Instructor & Lead Developer & CO-Founder of Cyber Academy For U
Penetration Tester & Security Researcher specializing in offensive security, web and network application security. Holder of eCPPTv3, eWPTXv3, eJPTv2, and CCEP certifications. Owner of cybera4u.com
View profileReviews
No reviews yet — be the first.
Write a review
Related learning
Certified Web Application Pentesting (CWAP)
A hands-on web application penetration testing course covering reconnaissance, Burp Suite, OWASP ZAP, XSS, SQL injection, common web attacks, file attacks, web services, CMS security, and evasion techniques.
Cybersecurity Fundamentals Roadmap
Roadmap that uses this course
Linux Administrator Roadmap
Roadmap that uses this course
AWS Security Roadmap
Roadmap that uses this course
Network Administrator Roadmap
Roadmap that uses this course
CTF Arena
Practice with scored challenges
Cybersecurity hub
Offensive and defensive paths
IT education hub
Networking, Linux, cloud, and more