Certified Web Application Pentesting (CWAP)
A hands-on web application penetration testing course covering reconnaissance, Burp Suite, OWASP ZAP, XSS, SQL injection, common web attacks, file attacks, web services, CMS security, and evasion techniques.
 Aws Alsalamat
- مبتدئ
- ~60 س
- العربية والإنجليزية
- آخر تحديث أكتوبر 2026
ماذا ستتعلّم
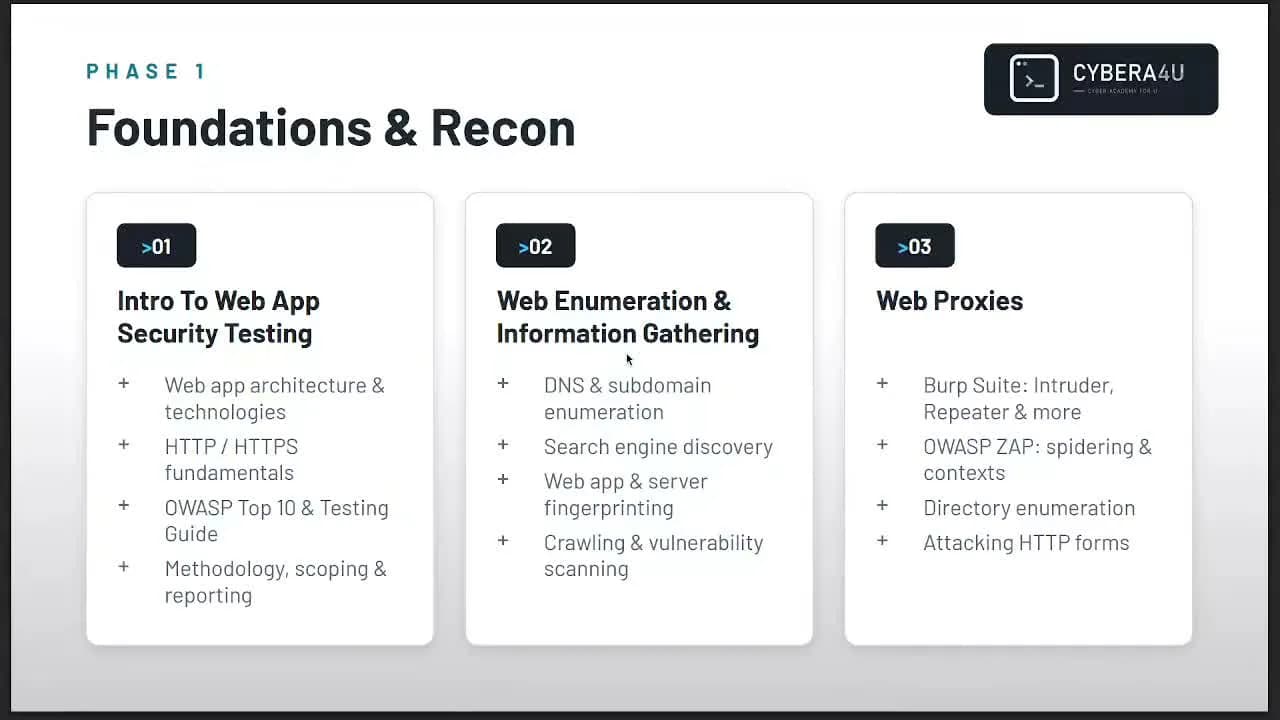
- Web application architecture and HTTP/HTTPS fundamentals
- Apply web application security testing methodologies
- Perform DNS and subdomain enumeration
- Conduct web application and server fingerprinting
- Use Burp Suite and OWASP ZAP for web security testing
- Identify and test XSS vulnerabilities
- Identify and test SQL injection vulnerabilities
- Test authentication
- sessions
- HTTP methods
- and CSRF
- Test file uploads
- path traversal
- LFI
- and RFI
- Assess SOAP
- REST
- XML-RPC
- and JSON-RPC web services
- Perform WordPress and CMS security testing
- Understand encoding
- filtering
- WAF
- proxy
- and IDS evasion basics
عن هذه الدورة
Certified Web Application Pentesting (CWAP) is a hands-on path designed to take learners from web application fundamentals to identifying and exploiting vulnerabilities using both manual techniques and automated tools.
The course follows a structured 10-module roadmap covering web application security testing, information gathering, web proxies, XSS, SQL injection, common attacks, file and resource attacks, web service security, CMS security, and encoding, filtering, and evasion.
Learners will work with industry-standard tools including Burp Suite, OWASP ZAP, SQLMap, XSSer, WPScan, and OWASP Amass.
The course emphasizes practical web application penetration testing methodology, from reconnaissance and manual testing to automated testing and vulnerability exploitation.
المنهج
لا وحدات · لا دروس · ~60 س إجمالًا
المتطلبات
- Basic familiarity with HTTP/HTTPS
- Basic familiarity with Linux
- Curiosity and a lab to practice in
لمن هذه الدورة
- Beginner web penetration testers
- Cybersecurity students
- Aspiring web application penetration testers
- Security professionals learning web security testing
- Learners interested in practical web application security
مدرّبك
Aws Alsalamat
Red Team & Blue team Specialized
I'm a cybersecurity graduate from Tafila Technical University with about four years of hands-on, self-directed experience in offensive and defensive security. I work as an instructor at Cybera4U, recording and delivering cybersecurity courses, and I did real-world PCI DSS vulnerability assessments with Banyamer Security. I'm ranked top 5% globally on TryHackMe with 345+ rooms completed, and I hold 14 certifications across pentesting, SOC analysis, and red teaming. I'm now looking for a junior SOC Analyst or Red Team role in Jordan or the MENA region.
عرض الملفالأسئلة الشائعة
What is the CWAP course?
Certified Web Application Pentesting (CWAP) is a hands-on course that takes you from web application fundamentals to identifying and exploiting vulnerabilities using manual and automated testing techniques.
What will I learn in this course?
You will learn web application security testing, information gathering, web proxies, XSS, SQL injection, common web attacks, file and resource attacks, web service security testing, CMS security testing, and encoding, filtering, and evasion basics.
How many modules does the course have?
The course contains 10 modules that progress from web security fundamentals and reconnaissance to advanced web application attack surfaces.
Which tools are covered in the course?
The course covers Burp Suite, OWASP ZAP, SQLMap, XSSer, WPScan, and OWASP Amass.
Do I need previous cybersecurity experience?
You should have basic familiarity with HTTP/HTTPS and Linux. You also need curiosity and a lab environment for practice.
Will I learn both manual and automated testing?
Yes. The course covers identifying and exploiting vulnerabilities manually before using automated tools to scale your testing.
Does the course cover XSS and SQL injection?
Yes. The course includes reflected, stored, and DOM-based XSS, as well as in-band and blind SQL injection techniques.
Does the course cover web reconnaissance?
Yes. You will cover DNS and subdomain enumeration, search engine discovery, web application and server fingerprinting, crawling, and vulnerability scanning.
Does the course cover advanced web attacks?
Yes. Advanced topics include file upload and filter bypass, path traversal, LFI, RFI, web service testing, CMS security testing, and WAF, proxy, and IDS evasion basics.
Who is this course for?
The course is designed for learners interested in web application penetration testing, including cybersecurity students, aspiring penetration testers, and security professionals developing their web security skills.
التقييمات
لا توجد تقييمات بعد، كن أول من يقيّم.
اكتب تقييمًا
محتوى تعليمي ذو صلة
Professional Ethical Hacking Track (PEHT)
Professional Ethical Hacking Track (PEHT) — a hands-on offensive security program covering reconnaissance, scanning, exploitation, and post-exploitation techniques used by real-world attackers.
Red Team Operator
مسار مهني
ساحة CTF
تدرّب على تحديات بنقاط
مركز الأمن السيبراني
مسارات الهجوم والدفاع
مركز تعليم تقنية المعلومات
الشبكات وLinux والحوسبة السحابية وغيرها